Local timeline
Currently: https://open.spotify.com/track/2mvabkN1i2gLnGAPUVdwek?si=e4b73efdc97b4c94 (Taylor Swift - Christmas Tree Farm)
🎅🎶
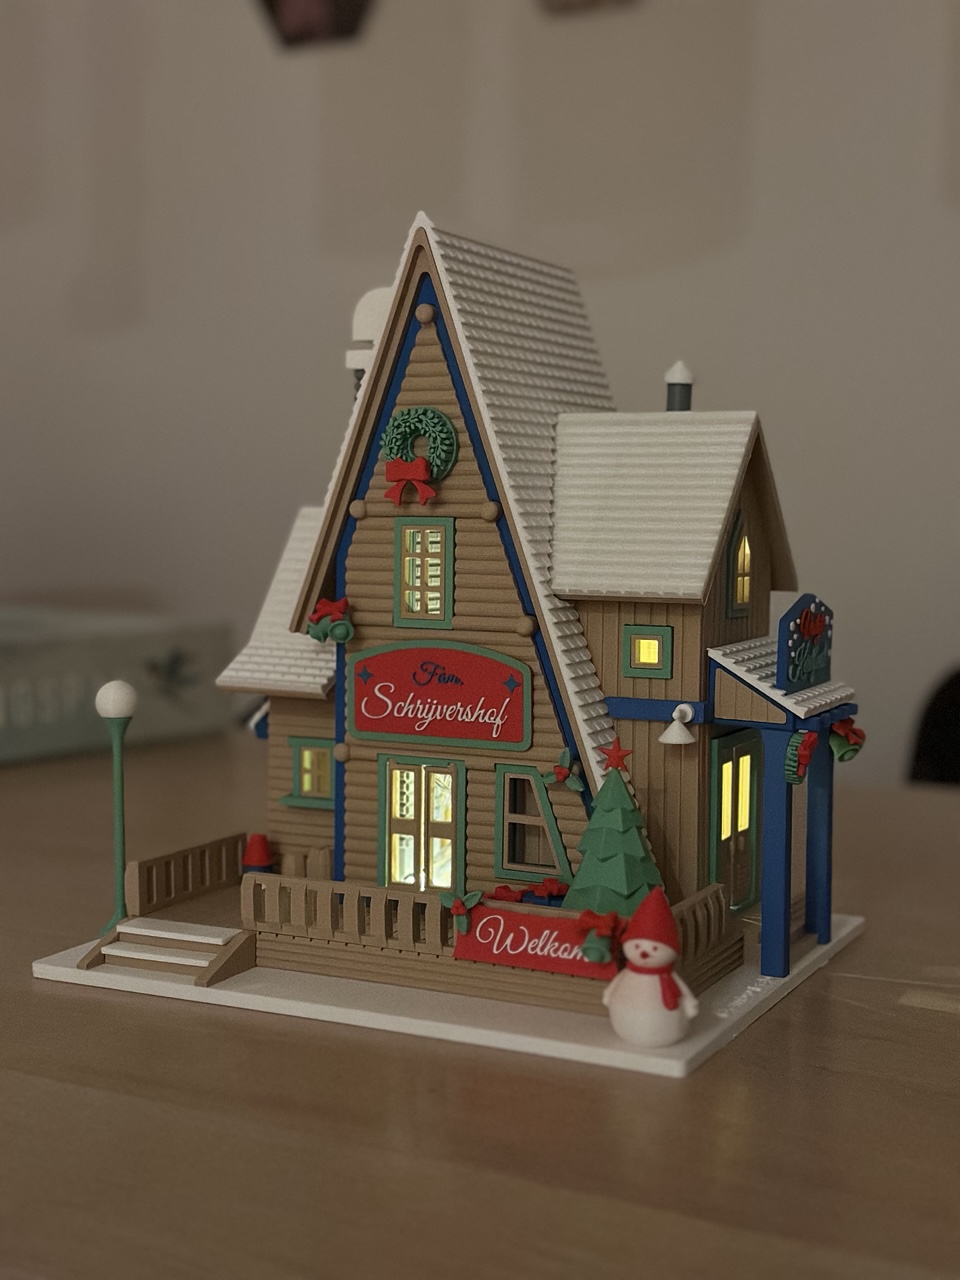
Finished 3D-printing a Christmas cabin. Really liking the outcome. The software allowed for easy changing of the included signs. #3DPrinting #BambuLabs
I do need to add that NFS is somewhat of an anti-pattern for Kubernetes. It's deemed unstable, and is bound to cause issues at some point. Locally in my homelab setup, I have a Synology CSI deployment that mounts block volumes using iSCSI.
For 1) you'll need https://github.com/kubernetes-sigs/nfs-subdir-external-provisioner
For 2) you can use my example. It's for mounting existing NFS shares to new Pods.
@stfn its Helm templating, so it's not directly mappable to regular Pod YAML. You define the NFS volume in the Pod spec, but the volumeMount in the container :)
Neat :-)
FYI: ingress.class annotation is deprecated. You should use the .spec.ingressClassName field instead.
You can mount NFS volumes directly to Pods. Here's a Helm values snippet that I use for my Plex server hosted on Talos Linux:
extraVolumes:
  - name: media-volume
    nfs:
      server: 192.168.1.5
      path: /volume1/media

extraVolumeMounts:
  - name: media-volume
    mountPath: /volume1/media
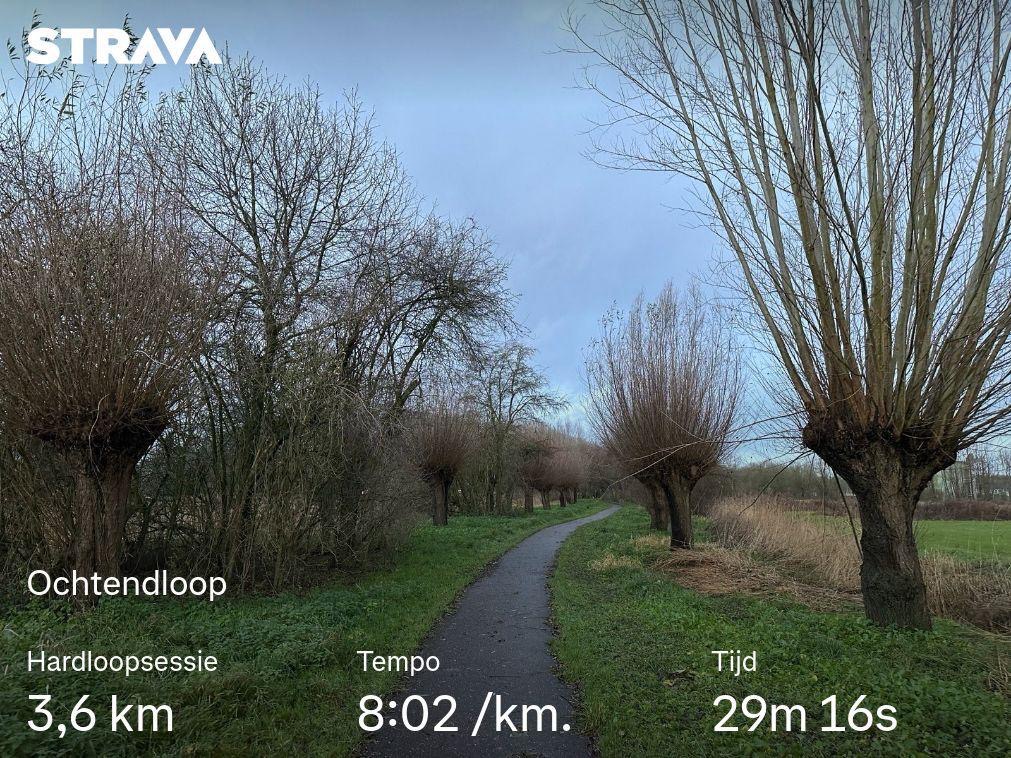
Tiny sprint intervals to get ready for my first 10K race tomorrow. Hope to finish it under an hour 🤞#running
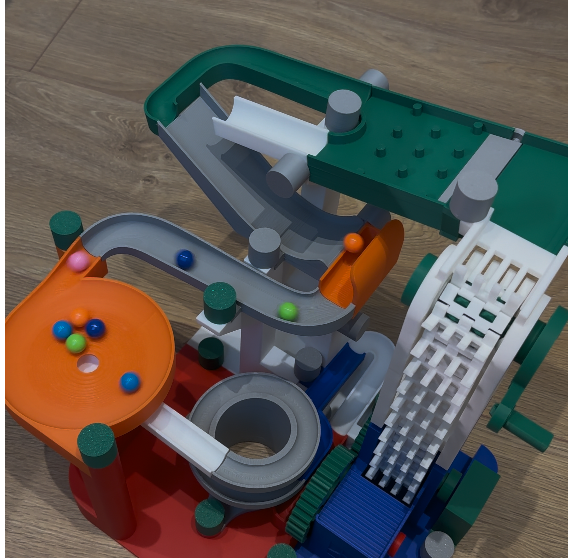
The 3D-printed marble track came out great. Perhaps I've been enjoying this a bit more than the kid itself.
No, you'll lose the k3s LB. It's not very economical to have one LB per service, as most cloud providers charge you for IPs/LBs. For HTTP(s) traffic you'll want to read up on an Ingress Controller. It's a reverse proxy deployment that looks for "Ingress" resources on your cluster, and it will configure the reverse proxy / vhost so you can expose that service/deployment through the Ingress Controller.
The Ingress Controller will handle TLS. It'll look somewhat like World -> Cloud LB -> (Service ->) Ingress Controller -> Service -> Pods.
https://kubernetes.io/docs/concepts/services-networking/ingress/